Thursday, November 19, 2026

01Top stories

Primary intelligence

Broadcom patches exploited critical VMware vCenter authentication bypass

Monitoring Track this incident

Broadcom issued VMSA-2026-0009 on November 19, patching five vulnerabilities across VMware vCenter, SDDC Manager and VMware Tools. The most urgent is CVE-2026-123890, a 9.8-rated VMware Directory Service authentication bypass that could let a network-reachable attacker obtain unauthorized vCenter access. Broadcom lists no workaround, making patched releases the primary defense.

The response matrix lists vCenter 8.0 U3m, 9.0.2.0200 and 9.1.1.0200 among fixed versions. Separate reporting says Google/Mandiant identified earlier exploitation by a suspected espionage actor, but the scale of compromise is not established.

Why it matters

A network-reachable management-plane authentication bypass can compromise control of an organization's virtual infrastructure.

via Broadcom advisory & VMware FAQ
Read full briefing Collapse briefing

Detailed briefing

Management-plane exposure

vCenter controls virtualization hosts, virtual machines and administrative operations, so compromise of its authentication boundary can have effects beyond a single workload. Broadcom describes the vulnerable component as VMware Directory Service and specifies network access to the affected vCenter service as the prerequisite. The advisory also includes separate SDDC Manager SQL injection, command injection and privilege-escalation issues, plus a VMware Tools SAML signature bypass. These are distinct vulnerabilities and should not be conflated with the authentication bypass.

Fixed versions and response

Broadcom's November 19 response matrix lists fixes for vCenter 8.0 and supported 9.x and Cloud Foundation branches, with special support guidance for vCenter 7 under extended support. The critical authentication bypass has no published workaround. Operators should identify affected management appliances, restrict management-network exposure where possible, apply the exact vendor patch for their branch and review authentication and administrative activity for anomalies.

Exploitation and uncertainty

Google Threat Intelligence and Mandiant reportedly observed exploitation before public disclosure and described tooling associated with a suspected espionage actor. That account increases urgency but does not establish the number of affected enterprises. The first-party advisory confirms the vulnerability and remediation, not the broader campaign attribution. A detailed independent account of affected victims and completed patch deployments remains unavailable.

Limitations & caveats

The full scope of observed exploitation and patch adoption is unknown.
European Commission confirms AI-assisted cyberattack, with some applications still offline

Investigating Track this incident

The European Commission confirmed November 19 that an AI-assisted cyber campaign detected October 22 prompted it to take several internal applications offline. Most services have been restored, but some tools remain unavailable, and the investigation is continuing. Officials confirmed misuse of AI tools without identifying the attacker or detailing how the intrusion occurred.

Politico reported possible exposure of personnel information and disruption to administrative systems, but the Commission has not corroborated those details. Its spokesperson said there was no evidence of a breach affecting Commission staff as a whole; that is not a guarantee that no individual records were exposed.

Why it matters

A major public institution confirms real service disruption and AI-assisted attacker activity, while data exposure remains under investigation.

via Reuters & Associated Press
Read full briefing Collapse briefing

Detailed briefing

Incident and reporting timeline

The Commission says it detected the campaign on October 22 and launched an investigation and preventive shutdowns. It publicly confirmed the AI-assisted nature of the campaign November 19. The reported operational disruption lasted beyond the initial detection, but officials did not provide a complete per-application outage timeline. Publication date should not be confused with the incident's October occurrence.

Operational and data impact

Several internal applications were deliberately taken offline as a protective measure, and most were subsequently restored. Reports describe possible effects on translation, payroll, timesheets and reimbursement systems, but the Commission declined to confirm those specific systems. It also said it had found no evidence of a staff-wide data breach. The unknown number of affected individuals and remaining offline tools prevent a definitive blast-radius estimate.

What AI involvement establishes

Officials described the campaign as involving AI tools, but did not publish a reproducible technical chain or identify a particular agent or model. AI-assisted vulnerability discovery does not itself demonstrate autonomous end-to-end exploitation. The investigation is open, and claims about the attacker's identity, initial access and stolen records remain unverified.

Limitations & caveats

No verified attribution, technical entry point or comprehensive breach assessment.

02Also worth knowing

Rapid scan briefs
Securityvirtualizationreview.com

CISA flags exploited LiteLLM and legacy software vulnerabilities

CISA added four vulnerabilities to its Known Exploited Vulnerabilities catalog November 18, including a LiteLLM sandbox escape, Apache Axis, REDCap and Synology flaws. Inclusion reflects evidence of exploitation, not a shared attacker or a common incident.

LiteLLM operators should review exposure of the custom-code guardrail testing endpoint and the project's patched version guidance. The affected endpoint is especially relevant to organizations centralizing access to AI models.

via Technical reporting
Read full briefing Collapse briefing

Detailed briefing

Affected surfaces

The reported LiteLLM flaw involves escaping a Python sandbox through custom guardrail testing functionality. The other entries affect older Java web services, a research-data platform and NAS software. They represent distinct technical conditions and require product-specific patch decisions.

Prioritization

A KEV entry is a stronger exploitation signal than an unexploited CVE score, but it does not provide a victim count. Teams should prioritize internet exposure and sensitive credentials, verify vendor fixes and review suspicious access logs.

Securityft.com

European AI security debate intensifies after official incident confirmation

European security officials are warning that AI tools can shorten the time required to discover and exploit vulnerabilities. The European Commission's newly confirmed October incident supplies an operational example, but published accounts do not yet establish the exact tooling, exploit chain or scope.

The broader concern is defensive response time: patching, asset inventory and change management become more difficult as attackers automate discovery. Claims that AI patching caused unrelated recent outages remain unsupported.

via Financial Times reporting & Commission confirmation via Reuters
Read full briefing Collapse briefing

Detailed briefing

What is observed

Germany's cybersecurity agency reported increasing attack pressure and faster exploitation timelines, while the European Commission confirmed misuse of AI in its own October cyber incident.

What is not established

No evidence reviewed connects the recent unrelated cloud, banking, aviation or infrastructure incidents to a common AI-driven patching failure. Security trends should not be used as a substitute for individual incident root-cause analysis.

Daily briefing

01Top stories

Primary intelligence

Java4Shell exposes OpenJDK Base64 memory corruption

Monitoring Track this incident

Publisher-provided image for Java4Shell exposes OpenJDK Base64 memory corruption
Image: calif.io

Calif disclosed CVE-2026-114938, a critical memory-corruption vulnerability in the optimized Base64 decoder of affected OpenJDK builds. On certain x86-64 processors with AVX-512 VBMI, malformed padded input can trigger an out-of-bounds heap write. Researchers report pre-authentication remote-code-execution demonstrations against default configurations of Keycloak, Jira, Confluence, Jenkins, Artifactory and PingFederate, with other application-specific chains requiring authentication.

Patches were announced November 17. The vulnerability warrants urgent Java runtime inventory and updates, but the researchers' demonstrations do not prove every Java deployment is exploitable or establish widespread exploitation in the wild.

Why it matters

Critical runtime flaw with urgent patching implications.

via Calif technical investigation
Read full briefing Collapse briefing

Detailed briefing

The optimized intrinsic

The vulnerability is in hand-written HotSpot assembly used for accelerated Base64 decoding. A malformed padded tail can underflow the calculated output length and produce an incorrect vector write mask, allowing data to be written past the destination array before Java rejects the input.

Operational exposure

Application endpoints that decode attacker-controlled Base64, including authentication and upload paths, may expose the vulnerable routine. The researchers report different exploit chains for different products; the actual runtime, CPU and application configuration determine exposure.

Mitigation and uncertainty

Consult the vendor advisory and deploy patched Java builds. Calif also describes disabling the Base64 intrinsic as a temporary mitigation, but this can affect performance and must be tested. There is no verified broad exploitation count.

Limitations & caveats

CPU and runtime dependent; no verified widespread exploitation.

Equinor responds to cyberattack on corporate IT

Investigating Track this incident

Equinor said November 17 it detected an ongoing cyberattack against some internal IT systems and mobilized resources to contain it. Reuters reported disruption to internal applications and, citing an employee, to email. Norway's National Security Authority acknowledged the incident and said it was offering assistance.

The energy company explicitly reported no impact on oil and gas operations or production and no indication of data theft. The distinction is important: a corporate IT incident at a critical energy supplier is serious without implying that industrial systems or energy delivery have been compromised.

Why it matters

An active attack at a major energy supplier warrants close monitoring.

via Primary report
Read full briefing Collapse briefing

Detailed briefing

Verified operational scope

The company described internal IT effects and ongoing containment. Reuters reported internal email disruption, but the affected system inventory, start time and complete duration remain undisclosed.

Production and response

Equinor said its production was unaffected, and Norway's security authority confirmed it was aware of the situation. The attack should not be described as an industrial control-system compromise.

Unknowns

No attacker attribution, intrusion path, confirmed stolen data or final restoration time was established in the reporting reviewed. Additional company statements are needed to determine when containment is complete.

Limitations & caveats

Production unaffected; attacker and scope unknown.

02Also worth knowing

Rapid scan briefs
Securitystatus.optimizely.com

Optimizely confirms security fix after malicious web-snippet campaign

Optimizely has confirmed that an attacker exploited a vulnerability in its Web Experimentation platform to add malicious JavaScript to customer projects. The company says it fixed the vulnerability, removed injected code, secured affected accounts and added safeguards against unauthorized script delivery. Independent researcher Scott Helme reports that all 188 infected snippets in his observed sample were clean by November 16 at 23:11 UTC.

This is a material remediation update to the November 16 compromise, not a new incident. The number of visitors exposed to card skimming, cookie theft, cryptocurrency-address substitution or iOS exploit delivery remains unknown. Optimizely still labels the incident monitoring.

Monitoring Track this incident

via Optimizely incident statement & Report URI investigation and November 17 update
Read full briefing Collapse briefing

Detailed briefing

Provider confirms vulnerability and corrective actions

Optimizely's November 17 incident notice says an unauthorized party exploited a vulnerability in its experimentation product to add malicious JavaScript to some customer projects. It reports fixing the vulnerability, removing injected code, securing affected accounts and adding protections against unauthorized code delivery. The company has not yet published detailed technical root-cause mechanics or a full postmortem.

Observed cleanup timeline

Scott Helme's follow-up, posted November 17 at 09:17 UTC, reports that all previously infected Optimizely files in his observed set had been clean since November 16 at 23:11 UTC. He also reports several attacker domains were disabled or stopped responding. These observations support removal of the known malicious scripts but do not establish that every cached copy or downstream exposure was cleared.

Residual risk and engineering lessons

The attacker placed code inside the project-level JavaScript served through a trusted experimentation script, so organizations could expose visitors without changes to their own application repositories. The investigation documents wallet substitution, payment skimming, cookie theft and mobile exploit delivery, but it cannot measure all resulting losses. Organizations should review historical third-party script changes, browser security telemetry, content security policy and any affected visitor sessions. Optimizely's incident remains in monitoring.

Securitymicrosoft.com

Microsoft describes Perception security for agents

Microsoft introduced security capabilities under its Perception initiative, connecting agent identity, access governance and monitoring across its security products. The stated goal is to make autonomous activity visible and governable in enterprise systems.

The effectiveness of these controls depends on deployed integrations, identity boundaries and actual audit coverage; the available claims are first-party.

via Original reporting
Read full briefing Collapse briefing

Detailed briefing

Established development

Microsoft introduced security capabilities under its Perception initiative, connecting agent identity, access governance and monitoring across its security products. The stated goal is to make autonomous activity visible and governable in enterprise systems.

Evidence and implications

The effectiveness of these controls depends on deployed integrations, identity boundaries and actual audit coverage; the available claims are first-party. The practical impact should be evaluated against primary documentation and subsequent verified outcomes, rather than inferred from announcement language.

Securityblog.cloudflare.com

Cloudflare examines Quad9 withdrawal from France

Cloudflare published an analysis of Quad9's withdrawal from France, arguing that legal pressure on recursive DNS operators can affect global infrastructure. The underlying issue concerns jurisdiction, filtering requirements and operators' willingness to serve particular markets.

Cloudflare has a direct industry interest, so its interpretation is commentary rather than an independent legal finding.

via Original reporting
Read full briefing Collapse briefing

Detailed briefing

Established development

Cloudflare published an analysis of Quad9's withdrawal from France, arguing that legal pressure on recursive DNS operators can affect global infrastructure. The underlying issue concerns jurisdiction, filtering requirements and operators' willingness to serve particular markets.

Evidence and implications

Cloudflare has a direct industry interest, so its interpretation is commentary rather than an independent legal finding. The practical impact should be evaluated against primary documentation and subsequent verified outcomes, rather than inferred from announcement language.

Monday evening incident and developer briefing

01Top stories

Primary intelligence

Optimizely supply-chain attack delivers malware across 178 organizations

Monitoring Track this incident

Publisher-provided image for Optimizely supply-chain attack delivers malware across 178 organizations
Image: report-uri.ghost.io

Scott Helme identified 188 infected Optimizely Web snippets at 178 organizations on November 16, distributing cryptocurrency address substitution, payment-card skimming, cookie theft and iOS exploit payloads. Most observed scripts were cleaned by the final sweep; the full impact is unknown. The practical significance depends on the specific technical mechanism and the independently established scope, rather than headline counts or vendor claims. The remaining evidence gaps are important when assessing operational consequences.

Why it matters

Trusted third-party scripts can create cross-organization security exposure without direct compromises of each customer website.

via Primary investigation & BleepingComputer
Read full briefing Collapse briefing

Detailed briefing

Supply-chain mechanism

The investigation describes malicious code delivered through a third-party experimentation script. Because websites load those scripts in visitors' browsers, an attacker can reach users of multiple unrelated organizations without separately altering each organization's application code.

Observed payloads and uncertainty

The reported behavior included cryptocurrency-address replacement, card skimming, cookie theft and mobile exploit delivery. The researcher reported 188 infected snippets across 178 organizations, but that is not a verified number of compromised visitors. Most observed scripts were cleaned; full exposure and initial access remain uncertain.

Limitations & caveats

Initial access and total affected visitors remain unknown. A separate Optimizely service incident is not proven related.

Patched uBlock Origin universal XSS exposes extension trust boundary

Publisher-provided image for Patched uBlock Origin universal XSS exposes extension trust boundary
Image: iter.ca

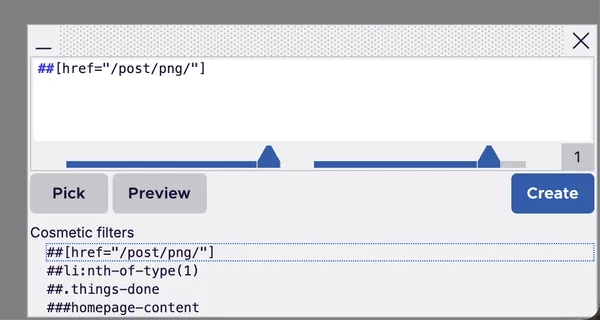
A Firefox Manifest V2 uBlock Origin element-picker vulnerability allowed malicious websites to trick users into adding trusted filters with script execution on other websites. It was patched. The practical significance depends on the specific technical mechanism and the independently established scope, rather than headline counts or vendor claims. The remaining evidence gaps are important when assessing operational consequences.

Why it matters

Browser extension UI must isolate untrusted website content from privileged configuration.

via Research write-up & Security advisory
Read full briefing Collapse briefing

Detailed briefing

The extension trust boundary

The disclosed Firefox Manifest V2 uBlock Origin vulnerability involved untrusted website content influencing a privileged element-picker configuration workflow. With user interaction, the flaw could lead to script execution across sites.

Status and practical response

The vulnerability was patched. The advisory does not establish widespread exploitation. Extension developers should treat page-derived input as untrusted, and users should keep the extension updated.

Limitations & caveats

Requires user interaction; no widespread exploitation established.

Windows 11 diagnostic events reveal coding-agent usage telemetry

Publisher-provided image for Windows 11 diagnostic events reveal coding-agent usage telemetry
Image: xusheng.dev

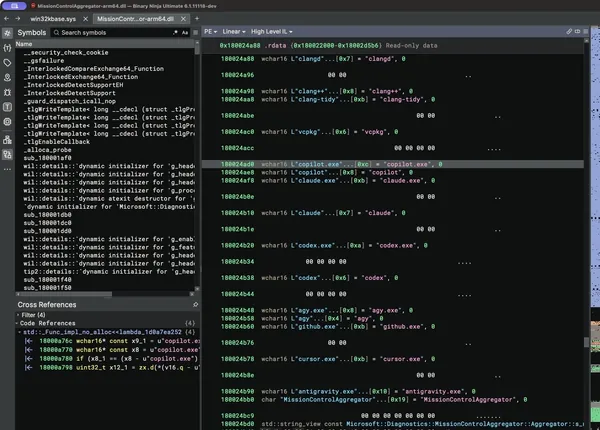
Reverse engineering found Windows diagnostics recording the presence of developer tools including Claude, Codex and Cursor. Optional diagnostics in tested configurations queued usage metadata for upload, without observed prompts or source code. The practical significance depends on the specific technical mechanism and the independently established scope, rather than headline counts or vendor claims. The remaining evidence gaps are important when assessing operational consequences.

Why it matters

Usage metadata may expose professional development workflows even when code content is not collected.

via Independent investigation
Read full briefing Collapse briefing

Detailed briefing

What the researcher observed

An independent Windows 11 investigation found diagnostic events indicating use of coding agents and developer tools, including Claude, Codex and Cursor, in tested configurations.

What was not shown

The report did not establish collection of prompts or source repositories, nor equivalent behavior on every Windows installation. Application-use metadata can still reveal development practices, so privacy-sensitive organizations should examine diagnostic settings and actual endpoint telemetry.

Limitations & caveats

Findings apply to specific tested builds and settings, not all Windows installations.

02Also worth knowing

Rapid scan briefs
Securitygithub.blog

GitHub AI Scan gains REST API management

Organizations can manage AI Scan settings through APIs, useful for repository security policy automation. This is a scoped development rather than evidence of a broader industry trend; practical consequences depend on deployment, adoption and independently verified results.

via GitHub changelog
Read full briefing Collapse briefing

Detailed briefing

What is established

Organizations can manage AI Scan settings through APIs, useful for repository security policy automation.

Interpretation and limitations

The reported development is worth monitoring, but the cited source does not establish every downstream outcome. Verify exact versions, access conditions and operational effects before relying on it in production or treating it as an industry-wide change.

November 14 briefing · Reconstructed

01Also worth knowing

Rapid scan briefs
Securitygithub.blog

GitHub AI security

The briefing surveyed GitHub's work on security checks for AI-assisted development, including secret scanning and workflow safety.

via GitHub security changelog

Morning briefing · Reconstructed from original topics

01Also worth knowing

Rapid scan briefs
Securitygithub.blog

GitHub secret scanning adds Cloudflare service tokens

GitHub's secret scanning now detects Cloudflare Access service tokens to help flag inadvertently published credentials.

via GitHub changelog

02AI & tooling in practice

Hands-on applications
Securitygithub.blog

GitHub Secret Scanning with Cloudflare token detection

Inspect the Cloudflare Access service-token detector in GitHub secret scanning if using Cloudflare Access service credentials.

Publisher-provided image for GitHub Secret Scanning with Cloudflare token detection
Image: github.blog
Detector release

Earlier Security coverage